 James
Last quarter, my team finished building an internal AI-powered support assistant for our customer success team. We spent weeks tuning prompt templates, testing response accuracy against our internal knowledge base, and setting up basic guardrails to block direct requests for sensitive system data. We didn’t run a full security review until two days before we planned to roll the tool out to our team. That’s when we discovered a critical gap: small, unintended variations in how users phrased prompts—even ones that felt nearly identical to our test cases—caused the assistant to pull in unredacted internal vendor documentation that contained private contact information for our enterprise clients. We had to push the launch back by a week to fix the issue, which delayed our team’s workflow and added unplanned work.
- Shifting Security Left: Mapping Risks Before Writing Code
- Building an Automated Test Suite and Integrating It into CI/CD
- Ongoing Maintenance: Shift Left Is Not a One-Time Fix
- FAQ
- 1. Does shifting security left eliminate all AI data leak risks?
- 2. How do you incorporate security reviews into the planning phase of an AI project?
Shifting Security Left: Mapping Risks Before Writing Code
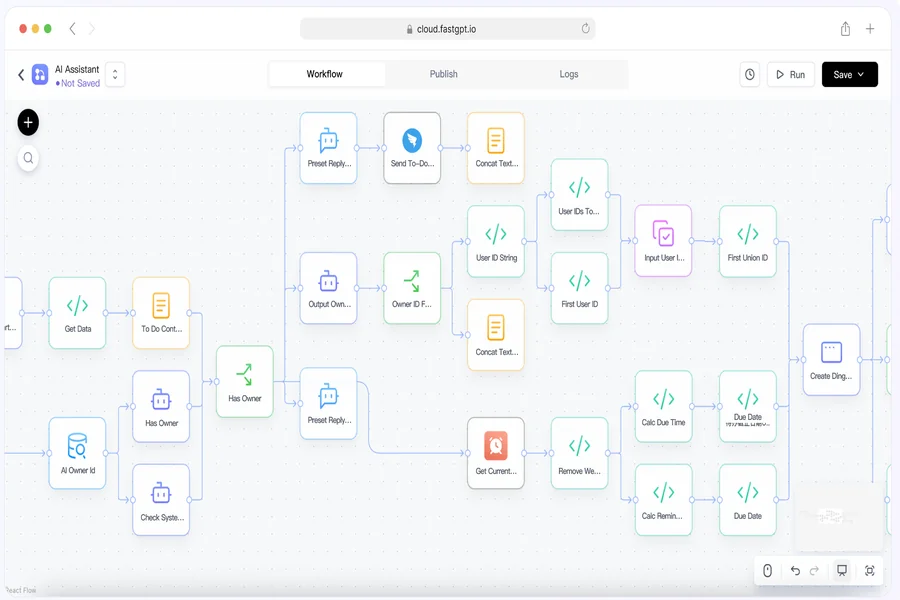
After that mishap, we decided to shift our security review process left for all future AI tooling, rather than waiting until the final stages of development. First, we mapped out all the potential user prompt patterns that our assistant would encounter, including common paraphrases of standard support requests. We also realized we needed a better way to test for inconsistent model behavior, since we’d never accounted for the fact that identical prompts can sometimes lead to different outputs. That’s when we found guidance from the FastGPT project, which broke down the core reasons for this variability: context window fragmentation, subtle differences in how prompt text is parsed, and minor drift in model temperature settings even when configured to be static.
Building an Automated Test Suite and Integrating It into CI/CD
Using that framework, we built an automated test suite that generates hundreds of paraphrased versions of our core prompts, runs each through the assistant, and logs every response for review. We added explicit guardrails to filter out references to private client data, and integrated this test suite into our CI/CD pipeline so that any changes to the assistant’s prompt logic or knowledge base trigger a full round of tests before deployment. We also started including a dedicated security review step in our initial planning phase for AI projects, rather than treating it as a last-minute checkbox.
Ongoing Maintenance: Shift Left Is Not a One-Time Fix
It’s important to note that this approach doesn’t eliminate all risk of unexpected behavior or data leaks. Even with consistent prompt configuration, models can behave unpredictably due to external factors like cached query data, updates to underlying model weights, or slight variations in how input text is processed across different deployments. We still make a point to conduct periodic manual reviews of production responses, and have set up lightweight monitoring to flag any instances where the assistant pulls in unintended sensitive data. This shift left has cut down on last-minute surprises, but it’s still a critical part of our ongoing maintenance for AI tools.
FAQ
1. Does shifting security left eliminate all AI data leak risks?
No. Even with consistent prompt configuration, models can still behave unpredictably due to external factors such as cached query data, updates to underlying model weights, or slight variations in how input text is processed across deployments. Shifting left should therefore be combined with periodic manual reviews of production responses and lightweight monitoring to flag unintended sensitive data exposure as part of ongoing maintenance.
2. How do you incorporate security reviews into the planning phase of an AI project?
Include a dedicated security review step in the initial planning phase, which involves: mapping potential user prompt patterns, identifying paths to sensitive data, designing guardrail rules, planning automated testing approaches, and allocating time and resources for these activities in the project timeline—rather than treating them as a last-minute task before launch.
